If you’re setting it up for the first time, you can navigate to Analytics > Overview > Human risk intelligence > Enable human risk intelligence to go through the essential onboarding flow. This is enough to get you set up for the launch. The flow has three steps: Training strategy, Behavior-triggered interventions, and a final review before you enable the system.
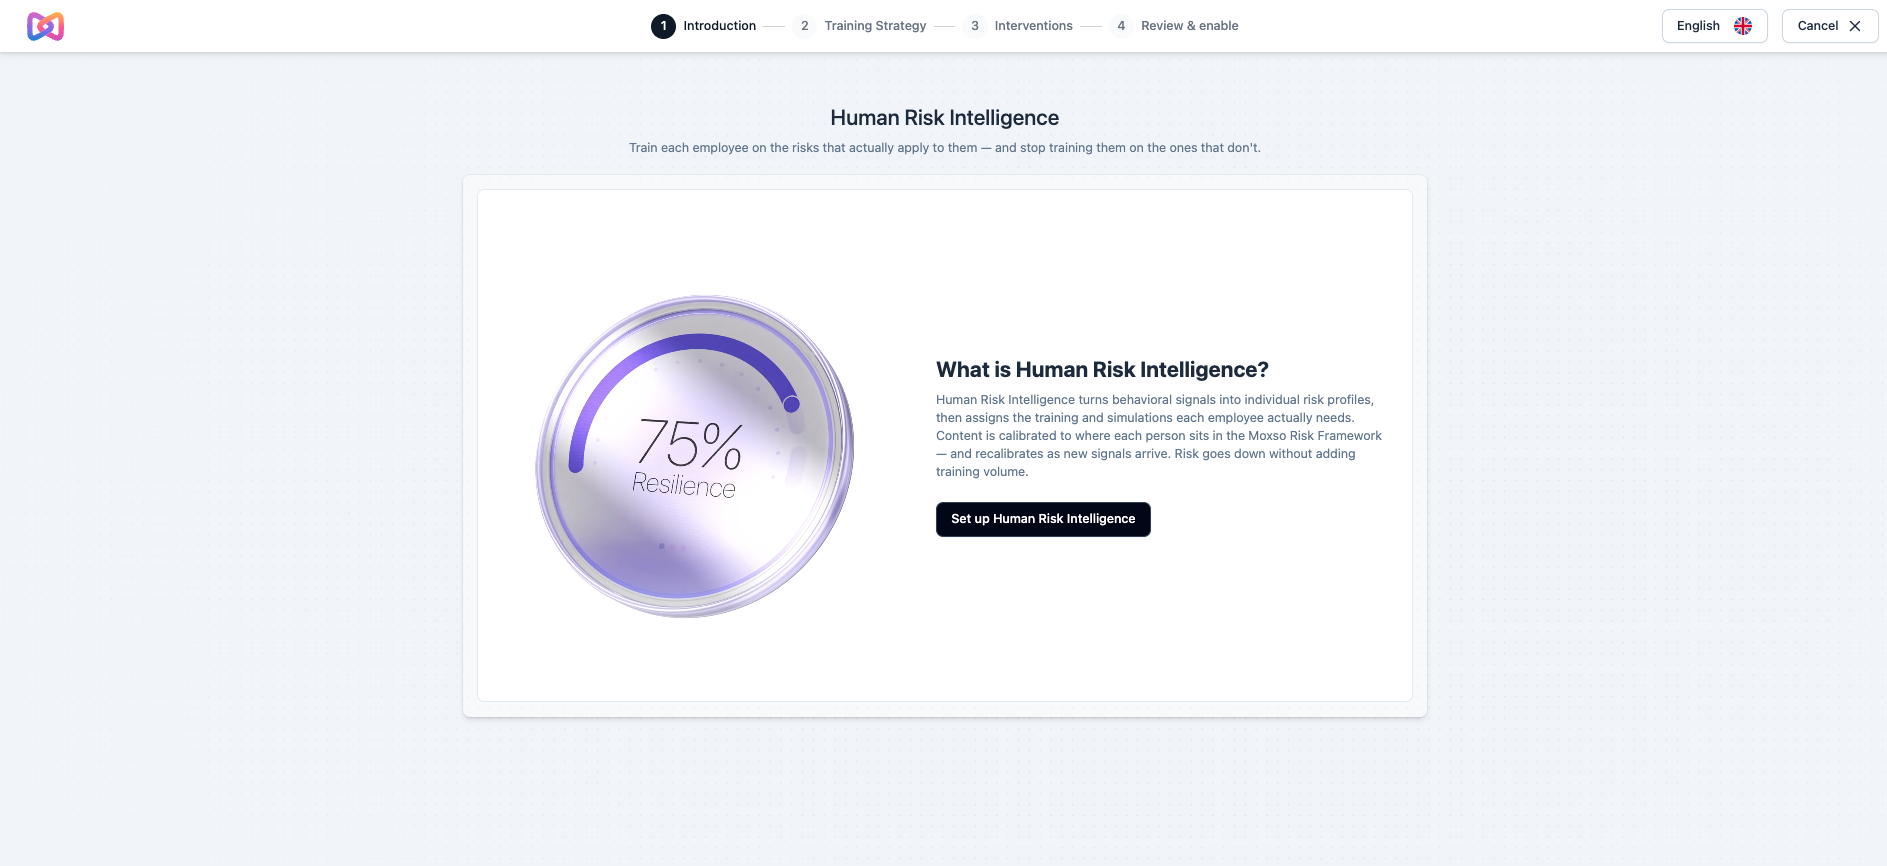
You can also set up and change HRI in Settings, where you'll find the advanced settings too. The settings are on two pages: Settings > Training for training, and Settings > Interventions for behavior-triggered interventions. This guide explains every setting on both pages.
Before you begin
HRI analyzes employee security behavior over time before it assigns training. No training is assigned right after you turn on automatic training. Moxso needs 24 hours to gather signals first. You can change your settings or switch the training mode at any time.
Training settings
Go to Settings > Training. These settings decide how training is assigned and delivered.
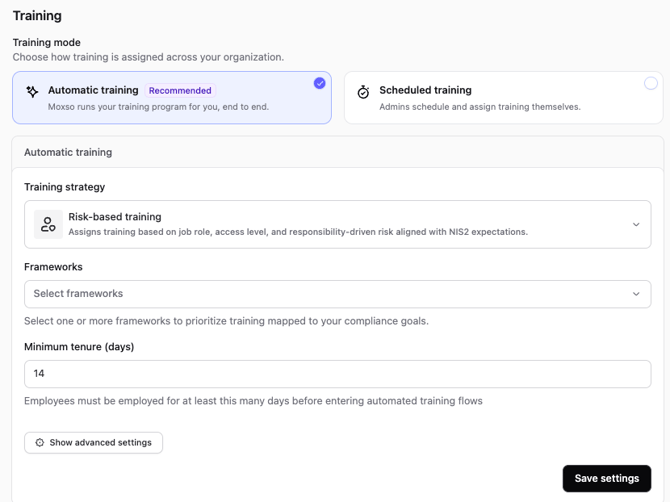
Training mode
- Automatic training (Recommended): HRI assigns training to each employee based on their signals and risk profile. This replaces the Enable Human Risk Intelligence setting.
- Scheduled training: admins schedule and assign training themselves. When you switch, Moxso asks you to confirm, stops assigning training, and keeps the assignments that already exist. The automatic training settings are hidden in this mode.
Training strategy
Select the strategy that matches your organization's priorities:
- Risk-based training: assigns training based on each employee's job role, access level, and responsibility. Aligned with NIS2 expectations. Choose this if reducing individual risk is your main goal.
- Compliance training: assigns training to meet the documented requirements in ISO 27001, SOC 2, and related frameworks. Choose this if keeping compliance coverage is your main goal.
- Group-based training: adjusts training using behavior trends across teams and departments, without targeting individuals. It doesn't use individual roles, access levels, or responsibility. Choose this if you prefer not to profile employees individually.
The resilience score is still calculated for each employee, even with group-based training.
Moxso can assign organizational roles to employees automatically, based on their department and group data. This is set up under Settings > Workspace > Employee data enrichment, not on the Training page. If it isn't turned on, Moxso uses the Administration role. See What are organizational roles?.
Frameworks
Select one or more compliance frameworks to map your training to: NIS2, ISO 27001, and SOC 2. You can combine them. For example, selecting NIS2 and ISO 27001 aligns the training to cover both.
Minimum tenure (days)
Employees must have been active in Moxso for at least this many days before they're included in automatic training. The default is 14 days.
Advanced settings
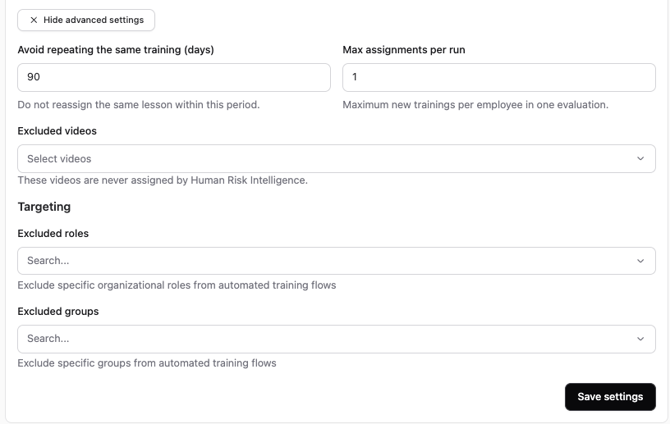
Click Show advanced settings to see more options.
|
Setting |
What it does |
Default |
|---|---|---|
|
Avoid repeating the same training (days) |
Stops the same video or course from being assigned again to an employee within this period. |
90 |
|
Max assignments per run |
The maximum number of new training assignments per employee each time HRI runs. |
1 |
|
Excluded videos |
Videos that HRI never assigns, to anyone. Everyone stays eligible for automatic training, but these videos are left out. |
None |
|
Excluded roles |
Employees with these roles aren't included in automatic training. |
None |
|
Excluded groups |
Employees in these groups aren't included in automatic training. |
None |
Click Save settings at the bottom of the training settings. The notification settings below have their own Save settings button.
Notifications
- Enable notifications: employees receive an email when new training is assigned. On by default.
- Notification cadence: how often reminder emails are sent after training is assigned:
- Loose: reminders 28 and 14 days before the deadline, plus a 3-days-left reminder, a last-day reminder, an overdue reminder, and a missed-deadline reminder.
- Normal: reminders 28, 21, 14 and 7 days before the deadline, plus the same 3-days-left, last-day, overdue, and missed-deadline reminders.
- Intense: the same reminders as Normal, plus a 1-day-left reminder.
- Smart reminders: Moxso keeps sending reminder emails until the employee completes the training. On by default.
Click Save settings.
Behavior-triggered interventions
Go to Settings > Interventions. Interventions decide which behavioral signals start an immediate response outside the regular training, such as a notification to the employee's manager or an alert to your security admins.
Turn on Enable interventions to see all the settings.
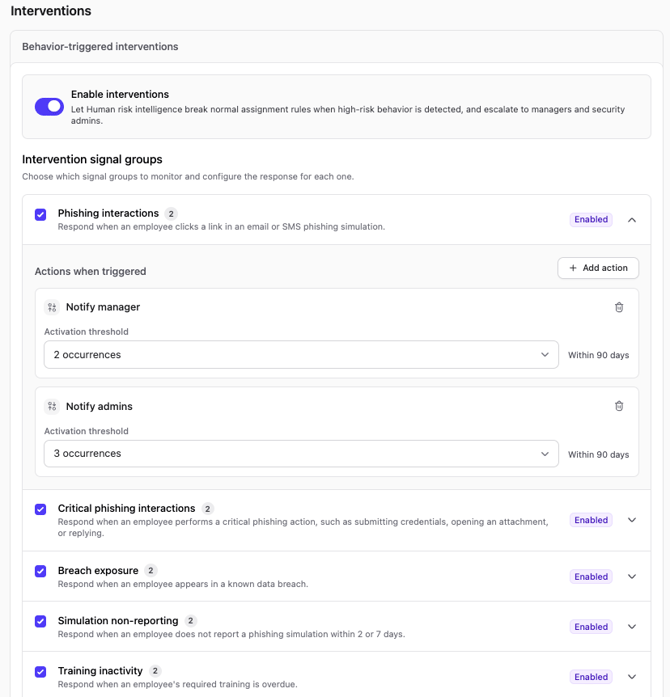
Intervention signal groups
Choose which signal groups to monitor. You can turn each group on or off, and expand it to set up its actions:
- Phishing interactions: an employee clicks a link in an email or text message phishing simulation.
- Critical phishing interactions: an employee does something critical in a phishing simulation, such as submitting credentials, opening an attachment, or replying.
- Breach exposure: an employee appears in a known data breach.
- Simulation non-reporting: an employee doesn't report a phishing simulation within 2 or 7 days.
- Training inactivity: an employee's required training is overdue.
For each signal group, click Add action to add a response:
- Notify manager: alerts the employee's manager.
- Notify admins: alerts your security admins.
- Assign new lesson: assigns corrective training to the employee.
- Notify employee: emails the employee about the behavior.
Depending on the signal group and the action, an action starts after a set number of occurrences within a time window, on a recurring time period, or on every occurrence. These are the default values:
|
Signal group |
Notify manager |
Notify admins |
|---|---|---|
|
Phishing interactions |
2 occurrences within 90 days |
3 occurrences within 90 days |
|
Critical phishing interactions |
1 occurrence within 90 days |
2 occurrences within 90 days |
|
Breach exposure |
Every occurrence |
Every occurrence |
|
Simulation non-reporting |
2 occurrences within 90 days |
3 occurrences within 90 days |
|
Training inactivity |
Every 30 days |
Every 60 days |
You can change the number of occurrences and the time periods for each signal group and action.
Exclusions
- Excluded roles: employees with these roles never receive interventions.
- Excluded groups: employees in these groups never receive interventions.
Click Save settings.